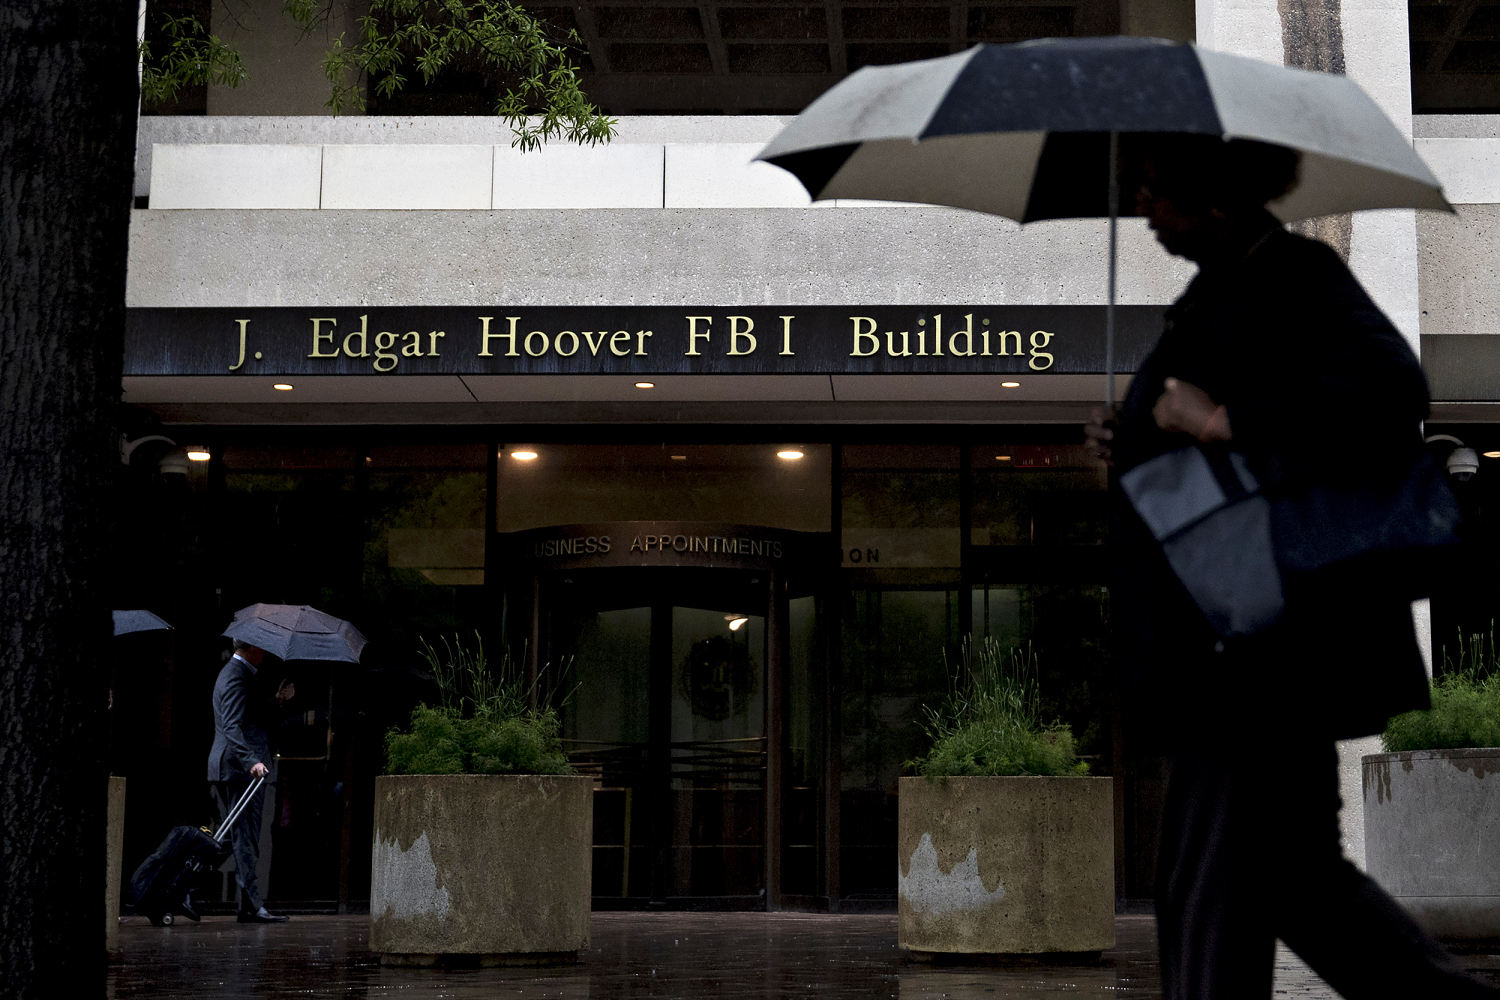
Public-facing recruitment portals sit at a structural fault line between external accessibility and internal data sensitivity, making an apparent breach of a law enforcement jobs site—accompanied by threat actor claims of stolen employee data—an immediate test of perimeter isolation, identity governance, and counterintelligence triage. When an investigation begins into a suspected intrusion on a career portal, the core analytical challenge is separating verifiable exfiltration from bluffing or peripheral data exposure while preventing lateral movement into core operational networks. This analysis establishes a four-part operational model for evaluating such incidents: the Perimeter-to-Core Topology, the Threat Claim Verification Matrix, the Personnel Risk Cost Function, and the Containment and Verification Sequence.
The Perimeter-to-Core Topology
Standard news reporting treats a "jobs website" as a single digital asset, blurring the boundary between outward-facing web applications and internal enterprise systems. In practice, a recruitment portal operates across distinct architectural tiers, and the security implications of an intrusion depend heavily on where the boundary was crossed. Read more on a related issue: this related article.
Tiered Exposure Across Public and Internal Zones
An applicant-facing career site is engineered for high availability and broad public reach. That design objective inherently expands the attack surface through web forms, file upload handlers, session management endpoints, and third-party integrations such as applicant tracking modules, content delivery networks, or analytics scripts. Even when an organization enforces strict network segmentation, an exposed web tier can become a beachhead if input validation fails, authentication tokens are mishandled, or an underlying application component suffers from an unpatched vulnerability.
The critical distinction lies in how employee records reach—or remain isolated from—that tier. In many architectures, public job portals hold applicant submissions, resume attachments, and recruiter workflows rather than full personnel rosters. When threat actors claim to possess sensitive employee data following an incident tied to a jobs site, several distinct architectural mechanisms could explain the claim: More analysis by Wired explores comparable perspectives on the subject.
- Shared or adjacent data stores: A recruitment platform may share database infrastructure, identity providers, or reporting pipelines with human resources or internal directory services, allowing an intrusion in one zone to expose records from another.
- Lateral movement across segmented boundaries: An initial foothold on a public web server may serve as a staging point to probe internal APIs, service accounts, or administrative consoles if network controls or credential hygiene are weak.
- Stale or co-located artifacts: Legacy test environments, exported spreadsheets, or employee contact lists used for hiring outreach can occasionally reside on servers or cloud buckets connected to recruitment operations.
- Fabrication or repackaging: Threat actors routinely pair a real—or minor—web incident with recycled, scraped, or wholly fabricated datasets to inflate extortion leverage and attract media attention.
A known operational fact in incident response is that an active investigation confirms inquiry and scrutiny, not proof that every claim made by a threat actor is accurate. Whether the alleged employee records actually originated from the jobs portal, came from an unrelated compromise, or do not exist in the claimed volume remains an educated hypothesis until forensic artifacts corroborate the scope.
The Threat Claim Verification Matrix
When hackers assert they hold sensitive employee data after an apparent portal breach, defenders and analysts face an asymmetric information problem. Threat actors control the narrative at the outset, while defenders must verify evidence without tipping off adversaries or prematurely alarm staff. Evaluating credibility requires testing claims against four independent dimensions: provenance, schema fidelity, temporal consistency, and operational feasibility.
Provenance and Schema Fidelity
Threat actors seeking credibility frequently offer samples—partial rows, field names, or screenshots—to prove possession. Analysts examine whether the structure of those samples matches real personnel records or reflects generic formatting. Real internal records typically contain idiosyncratic identifiers, organizational codes, or specific null patterns that are difficult to guess cleanly without access to genuine data. Conversely, over-polished or generic fields—such as overly uniform phone formats or missing internal metadata—raise doubts about authenticity.
Temporal and Architectural Consistency
A claim must align with the timeline and technical reality of the system. If an intrusion occurred hours before a public boast, rapid exfiltration of massive structured archives is possible only under specific conditions, such as direct database access or pre-staged cloud snapshots. If the claimed data includes attributes that never touch the recruitment portal—such as sensitive background clearance files or internal operational assignments—the adversary must explain how they crossed from the hiring tier to those repositories. Unexplained leaps in access point toward exaggeration or a separate compromise elsewhere in the enterprise ecosystem.
Operational Feasibility and Counterintelligence Context
When a high-profile government or law enforcement agency is targeted, the stakes extend beyond standard corporate identity theft. Employee data in a law enforcement context carries counterintelligence value: names, roles, contact details, or organizational ties can assist hostile profiling, targeted spear-phishing, or intimidation campaigns. At the same time, high-value targets attract heightened noise from opportunistic actors and state-aligned groups alike. Treating every extortion claim as verified inflates panic, whereas dismissing a claim without forensic proof leaves personnel exposed if genuine data was taken.
The Personnel Risk Cost Function
Conventional breach commentary often reduces impact to a single headline number, such as records exposed or dollars spent. A more rigorous way to model the fallout of an alleged employee data breach is through a cost function with four interacting variables: Exposure Sensitivity ($S$), Targeting Multiplier ($T$), Detection Latency ($L$), and Containment Friction ($F$).
$$\text{Risk Cost} \propto S \times T \times L \times F$$
This relationship is multiplicative rather than merely additive because a failure in one dimension amplifies the damage of the others.
- Exposure Sensitivity ($S$): Basic business contact details carry far lower personal risk than Social Security numbers, home addresses, financial details, health records, or security-sensitive role indicators. Even small volumes of high-sensitivity fields create outsized harm.
- Targeting Multiplier ($T$): For law enforcement personnel, ordinary identity fraud is compounded by targeted harassment, doxxing, or adversary reconnaissance. Data that might look routine in a commercial setting becomes actionable intelligence when paired with an individual's agency affiliation.
- Detection Latency ($L$): The longer an intrusion goes unnoticed—or the longer it takes to determine what was actually accessed—the more time adversaries have to validate stolen data, launch follow-on phishing against employees, or pivot deeper into infrastructure.
- Containment Friction ($F$): Revoking compromised tokens, isolating web services, rotating credentials, and notifying affected staff introduce operational friction. In a live investigation, overly abrupt public disclosures or heavy-handed network cutoffs can complicate evidence preservation or disrupt legitimate hiring and operational workflows.
Consider a conceptual example where an attacker claims to have employee contact records and internal role data from a recruitment portal. Even if no financial numbers were taken, the combination of agency affiliation ($T$) and slow confirmation of what left the network ($L$) can drive targeted spear-phishing against staff whose work emails or personal details appear in the leak. Conversely, if forensics show the portal only handled public job applications and no employee records resided on that tier, $S$ drops sharply for internal staff, shifting the immediate exposure toward job applicants whose resumes and personal details were submitted through the site.
The Containment and Verification Sequence
Responding to an apparent breach of a public recruitment portal while hackers claim employee data requires disciplined sequencing. Rushing to patch before preserving volatile evidence can erase forensic proof, while waiting too long to harden exposed endpoints invites follow-on exploitation.
Step 1: Preserve Volatile Evidence and Lock Down Credentials
Incident responders first capture volatile system state—memory images, active network connections, process lists, and web/application logs—before rebooting or wiping affected nodes. Simultaneously, teams rotate credentials tied to the portal, database connections, API keys, and any identity federation links that touch internal directories. If an intrusion path is active, blocking malicious traffic at the edge and revoking suspicious sessions stops ongoing access without destroying historical logs.
Step 2: Reconstruct the Attack Path and Audit Data Flows
Investigators map the exact entry point—whether a vulnerable web application, misconfigured cloud storage, compromised administrator account, or third-party vendor integration—and trace every subsequent request. A critical part of this step is auditing outbound data transfers and checking whether any internal HR or employee tables were reachable from the compromised tier. Known facts from server and network logs must be separated explicitly from unverified claims made by the threat actor.
Step 3: Segment Hiring Infrastructure from Employee Repositories
A recurring structural weakness in organizations is allowing public-facing web applications too much visibility into internal systems. Hardening after a recruitment portal scare involves enforcing strict network segmentation, applying least-privilege access to service accounts, stripping unnecessary employee data out of outward-facing environments, and placing strong authentication and anomaly monitoring on administrative interfaces.
Step 4: Execute Tiered Notification and Personnel Guidance
Notifications should follow evidence rather than rumor. Once investigators establish which populations face credible risk—whether job applicants, current employees, or both—communications should specify what data types were actually implicated, what remains unconfirmed, and what concrete protective steps individuals should take, such as monitoring accounts, enabling multi-factor authentication, and treating unexpected messages referencing the incident with skepticism.
Limitations and Trade-Offs in Practice
No containment or verification playbook eliminates uncertainty overnight. Forensic attribution and exact exfiltration accounting can take days or weeks, especially when logs are incomplete or attackers use legitimate-looking requests that blend into normal web traffic. Public agencies also face a tension between transparency and investigative integrity: sharing too much detail too early can help adversaries refine future attacks or compromise ongoing law enforcement inquiries, while sharing too little fuels speculation and undermines trust among applicants and staff.
Strategic Play
Treat any hacker claim of stolen employee data following a recruitment portal probe as an unverified high-severity hypothesis until forensic data flow logs prove or disprove reachability between the public hiring tier and internal personnel stores—and immediately enforce architectural isolation so public recruitment applications can never serve as a stepping stone to employee records.