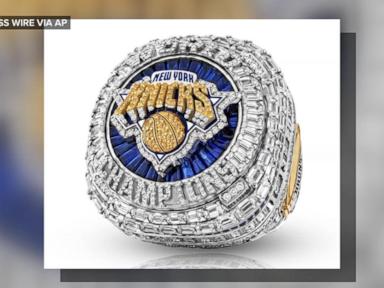
Reports linking New York Knicks coaches waiting on rings with staffers hit by a phishing email highlight two distinct administrative vulnerabilities inside a high-profile sports organization, one centered on post-season hardware fulfillment and the other on inbox security. No public evidence confirms that the two events share a single cause or timeline, yet together they expose how routine operations inside a modern franchise can stall or break down behind the scenes.
When a headline pairs championship or milestone rings with a phishing incident, readers naturally wonder whether a single breach disrupted merchandise logistics or whether two unrelated headaches hit the same front office at an awkward moment. In professional sports, those worlds rarely collide directly unless a vendor portal, shipping spreadsheet, or billing thread gets compromised. More often, they reveal parallel friction points: slow custom-manufacturing and distribution chains on one side, and human-targeted social engineering on the other. You might also find this connected article useful: What Happens When Twenty Thousand People Hold Their Breath Over a Song.
A hypothetical example illustrates how easily confusion spreads. Imagine a fictional front office where a logistics coordinator expects a tracking update from a custom jeweler while an IT security team circulates an alert about a spoofed message disguised as an operational notice. Without clear internal communication, staffers might assume a delayed ring shipment stems from a cyberattack, or treat a suspicious email as a routine vendor follow-up.
Why Championship and Milestone Rings Take Months to Arrive
Custom rings in professional basketball are rarely off-the-shelf items sitting in a warehouse waiting for a label. Designers, league approvals, sizing checks, engraving, gemstone setting, and tier allocations for players, coaches, front-office executives, and support staff stretch fulfillment across long production windows. As extensively documented in detailed coverage by ESPN, the effects are worth noting.
Even when a team moves quickly after an achievement or tournament milestone, ring tiers create bottlenecks. Coaching staffs often include head coaches, assistant coaches, player development specialists, video coordinators, and performance staff, each requiring exact measurements and roster verification. One late sizing sheet or a revision to an engraving detail can hold up a batch before production even begins.
Shipping adds another layer of delay. High-value items require insured transport, chain-of-custody tracking, and coordinated delivery windows rather than standard parcel drop-offs. When coaches are on the road during training camp, preseason, or regular-season road trips, coordinating handoffs or secure deliveries takes extra effort.
From an organizational standpoint, a delay in receiving rings looks dramatic from the outside, yet in front-office operations it is frequently mundane. Custom jewelry manufacturing runs on craftsmanship and approval cycles rather than instant retail speed. Still, when expectations run high around a team, any quiet wait invites speculation that something went wrong behind closed doors.
How Phishing Targets Sports Front Offices and Support Staff
Phishing attacks succeed because they exploit ordinary workplace habits rather than exotic technical flaws. Staffers across a basketball organization spend their days answering emails from agents, travel coordinators, league offices, vendors, sponsors, and colleagues. Attackers study those routines and craft messages that look familiar enough to earn a quick click or reply.
In a busy sports environment, urgency is a weapon. A message claiming an invoice needs immediate approval, a travel itinerary changed, a shared document requires login verification, or a vendor account was updated fits right into the daily rhythm of an athletic department. Speed is rewarded in sports operations, and attackers count on people acting fast before checking sender headers or links.
Credential Harvesting Versus Business Email Compromise
Security analysts generally separate everyday phishing lures into two practical tracks, though both rely on deception. Credential harvesting pushes a user toward a lookalike login page designed to capture usernames, passwords, and multi-factor prompts. Once an attacker holds valid credentials, they can read messages, search for financial or operational details, and launch follow-up attacks from inside a trusted account.
Business email compromise takes a subtler route. Instead of blasting obvious malware, an attacker monitors threads or impersonates a known contact to redirect payments, harvest sensitive roster or vendor lists, or trick staffers into sharing internal files. Even a single staffer falling for a convincing lure can create hours of remediation work for IT and legal teams.
Why Large Organizations Face Wider Attack Surfaces
Major sports franchises are not small family shops running off one shared inbox. They operate sprawling ecosystems spanning basketball operations, arena or business staff, analytics groups, medical and conditioning teams, communications departments, and external contractors.
More departments and more third-party tools mean more places where a convincing lure can land. A seasonal intern, a part-time coordinator, or a vendor contact may have different habits and training levels than a veteran executive. Attackers do not need to fool everyone in the building; they only need one moment of distraction from one person with useful access.
Where Ring Delays and Inbox Threats Actually Overlap
Separating myth from operational reality matters here. A phishing email sent to staffers does not automatically halt a jeweler's workshop, nor does a slow ring delivery prove an organization suffered a major system intrusion. Treating every operational hiccup as proof of a cover-up or a massive breach muddies how problems get fixed.
There is, however, a real intersection around information hygiene and vendor communication. Whenever custom awards, high-value shipments, or private personnel lists are coordinated over email, scammers look for openings. Any message promising exclusive updates, demanding login checks to view shipping details, or asking for personal information under the guise of logistics deserves scrutiny.
| Operational Area | Common Cause of Friction | Real-World Impact on Staff | Practical Safeguard |
|---|---|---|---|
| Custom rings and awards | Multi-tier sizing, approvals, insured shipping | Frustration and outside speculation during long waits | Clear status updates and verified delivery channels |
| Staff phishing incidents | Spoofed links, urgent requests, lookalike logins | Account lockouts, audits, heightened inbox caution | Hardware or app-based MFA and out-of-band checks |
| Vendor and roster coordination | High email volume across busy schedules | Confusion over legitimate vs. fraudulent notices | Standardized templates and strict approval rules |
The Gray Areas Behind Front-Office Reporting
Reports about Knicks coaches waiting on rings and staffers hit by phishing also show the limits of public sports coverage. Short items and video clips often condense complex internal processes into a punchy headline. What looks like a single story on a screen may actually bundle two separate tidbits picked up from different sources.
At the same time, franchises rarely share granular cybersecurity details publicly unless legally required or operationally necessary. Discussing exact phishing lures, targeted accounts, or defensive gaps in public can hand attackers useful feedback on what worked. Silence from a team is often standard incident-response discipline rather than proof of indifference.
There is also a gray area in how organizations measure security readiness. Training staffers with occasional simulated emails helps build awareness, yet over-relying on click-rate metrics misses deeper issues like weak recovery processes, shared logins, or over-privileged accounts. Real resilience comes from limiting what an attacker can reach even if someone slips up once.
Concrete Steps for Sports Staff and Organizations
For anyone working inside a sports front office, athletic department, or fast-moving media operation, the lessons from this pairing are straightforward and actionable.
- Verify high-stakes requests out of band. Confirm payment changes, credential prompts, or sensitive file requests over a known phone number or separate internal channel rather than replying directly to an unexpected email.
- Use phishing-resistant authentication. Pair strong unique passwords with authenticator apps or security keys so a stolen password alone cannot open an account.
- Keep operational updates structured. Give staffers clear, predictable channels for items like awards, travel, and equipment so employees do not have to guess whether an email is legitimate.
- Separate rumor from root cause. When two unrelated problems surface around the same time, investigate each one on its own facts before connecting dots that do not match.
High-visibility teams live under a magnifying glass where every delay and every misstep gets magnified, yet the hardest work of keeping an organization safe and running smoothly happens in the quiet habits people practice every single day.